
Cyber Intelligence, Investigation and Complex Information Searches
Advanced AI-Driven Cyber-Surveillance Platform
If there's a threat on the network, Teron has already spotted it.
Enthec platform's investigation module, which includes a powerful search tool for emerging threats, compromised assets, and adversaries, with AI-powered analysis
Intelligence Tool: the core that coordinates all research

All searches are performed automatically, continuously, and in real time.
- It is the core of the specialized research environment designed for intelligence analysts and strategic cybersecurity teams within governments and corporations, featuring an intuitive interface, multilingual search capabilities, and contextual analysis capabilities.
- It coordinates and controls the specialized research environment designed for intelligence analysts and strategic cybersecurity teams.
- It serves as the driving force behind the Teron cyber intelligence platform, enabling proactive and reactive investigations into potential threats, data breaches, exposed credentials, compromised infrastructure, malicious actors, and ongoing campaigns.
How does Teron work?
The platform processes and prioritizes hundreds of thousands of records daily, cross-referencing conversations from hacking forums, leaked databases, messaging channels, and illegal marketplaces.
Track
Teron scans thousands of sources at once: forums, peer-to-peer networks, illegal marketplaces, messaging channels, leaked databases, and compromised servers.
Enrich
Each finding is accompanied by additional information: where it comes from, what risk it poses, and whether it is related to other threats or active campaigns.
Apply AI
AI cross-references all findings, filters out noise, and delivers reliable, context-rich information.
Deliver
The investigator receives the results instantly and can jump from one piece of data to another to track a person or a case.
Analyze images
It recognizes logos, text, displayed credentials, and compromised control panels in any screenshot—in any language.
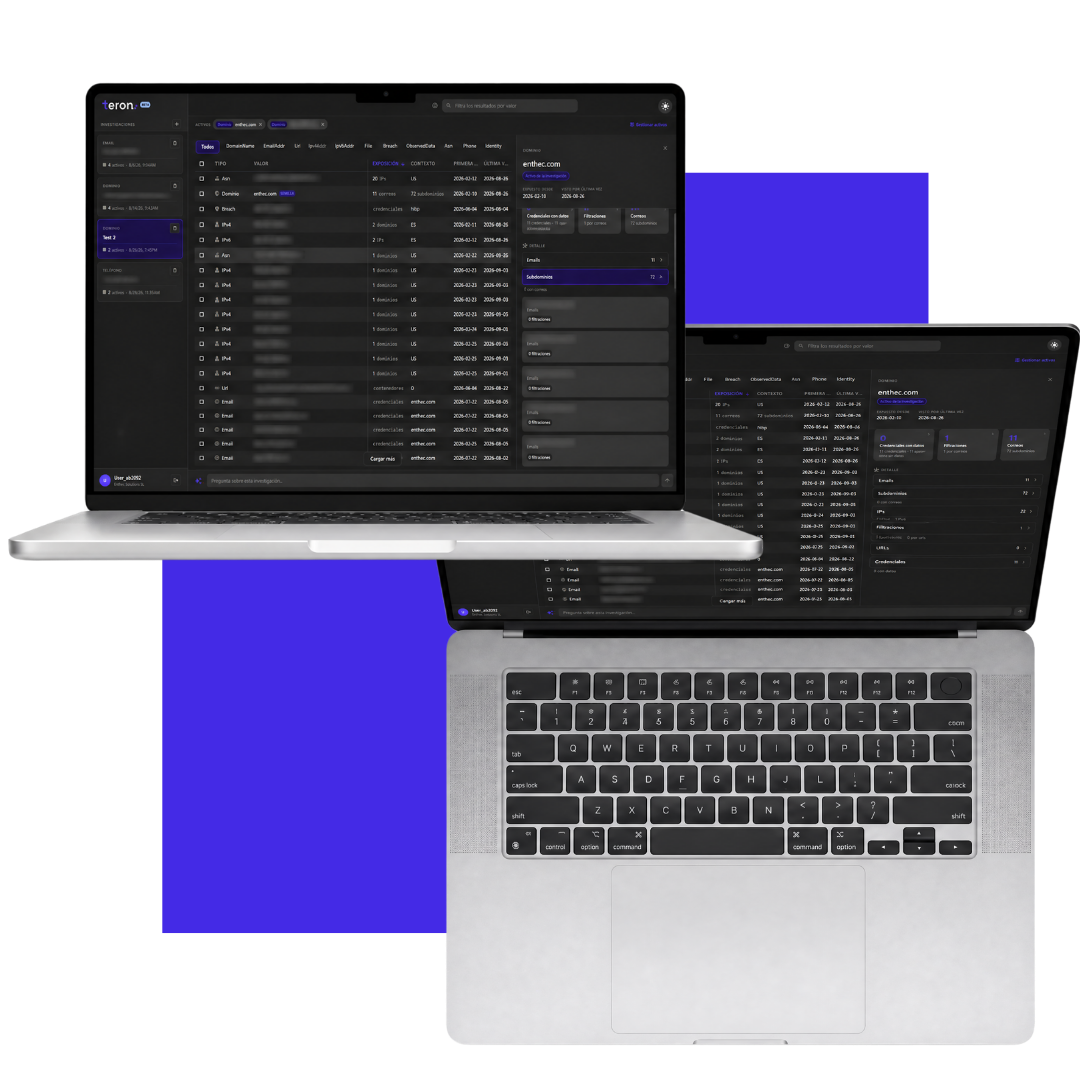
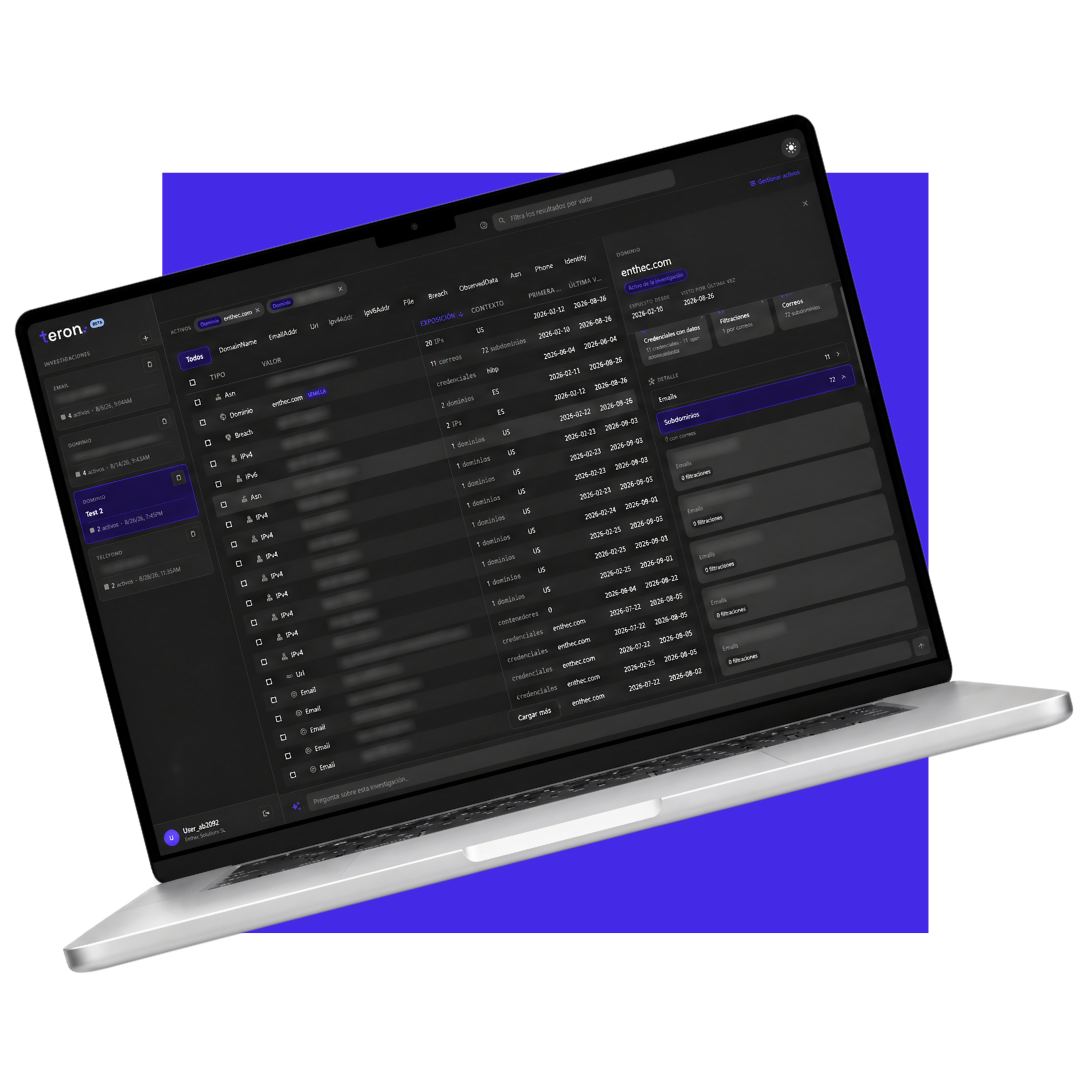
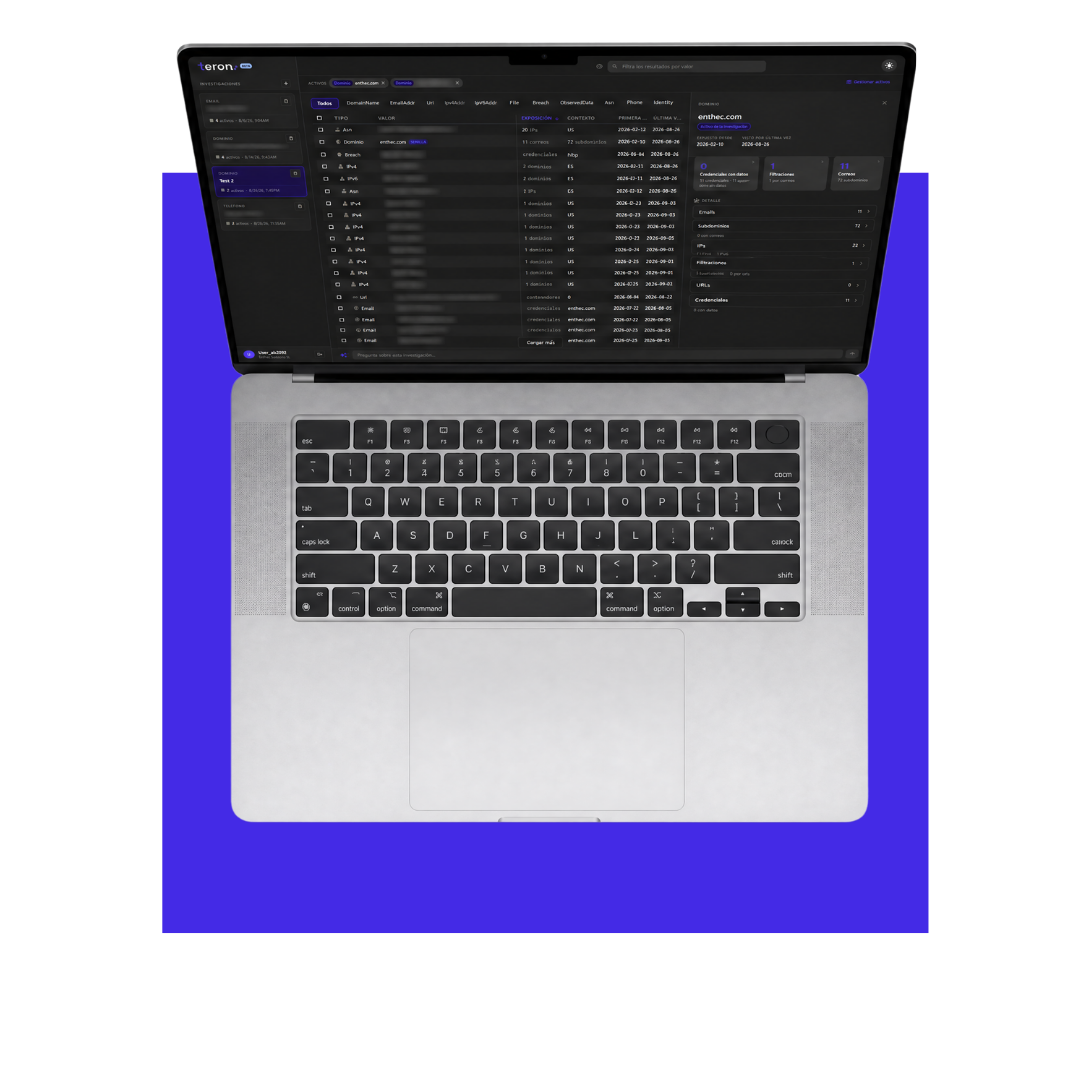
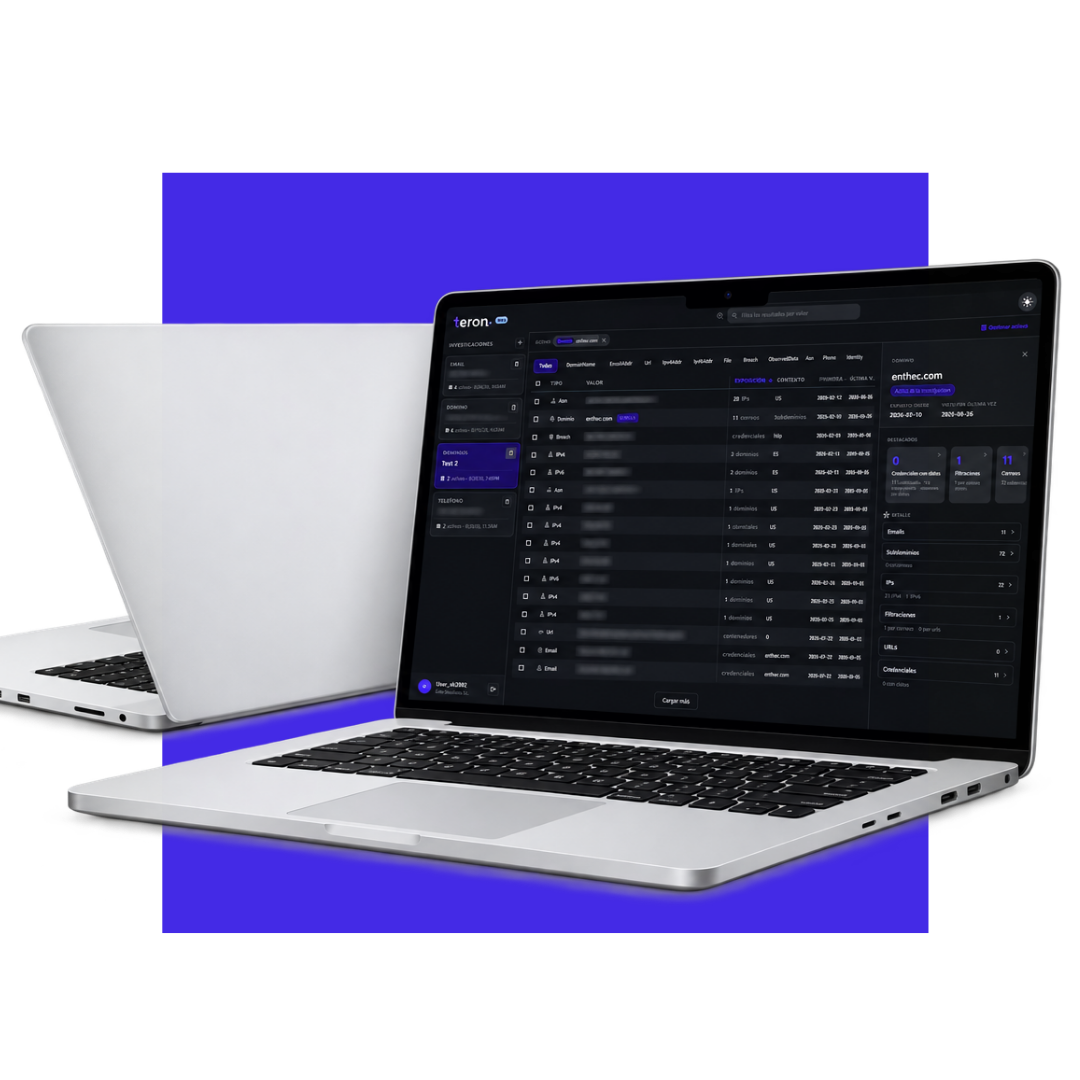
A partner who manages multiple clients can switch between clients without changing tools or sessions, and sees only the information relevant to them
Teron's Differential Factors:
- 100% European technology. All technology is developed in-house and is proprietary, completely independent of third parties and free of backdoors.
- Zero-trust architecture with European end-to-end encryption
- Compliance by design with all continental regulations
- European governance with independent oversight and audits
- A database unique in Europe for searching, correlating, and analyzingdata for the purpose of designing and implementing strategies for surveillance, control, defense, and attack in the digital context.
- A platform with cybersecurity standards audited by internationally renowned organizations such as AENOR (27001, high-level ENS)
- A commitment to the interests of digital autonomy and sovereignty, which are objectives of the European Union within the international geopolitical context.
What sets us apart?
100% European technology
Zero-trust architecture
Compliance by Design
European Governance
A database unique in Europe
Audited by AENOR
Cyber Threat Investigation Engine
- Peer-to-peer networks
- Cybercriminal forums
- Leaked databases
- Platforms for buying and selling initial access
- Messaging channels
- Compromised servers
Put Your Company to the TestIt costs nothing
Investigate a complete case, not a single consultation.
Each piece of research is saved, revisited, and shared.
One click—no need to log in again on the Enthec platform
Research and Intelligence Capabilities
Its ability to extract, analyze, and present data from hostile environments—in a secure, anonymized, and contextualized manner—enables two main types of activities:
Threat Anticipation
Anticipate threats, mitigate risks, and disrupt criminal activities before they turn into actual attacks.
Complex Investigations
Complex investigations related to organized crime, terrorism, disinformation, or digital espionage.
Unified Data Repository
The system scans a unified repository of data from the digital criminal environment, built from thousands of active sources: peer-to-peer networks, cybercriminal forums, leaked databases, platforms for buying and selling initial access, messaging channels, and logs from compromised servers. The results are returned in real time, enriched with technical and strategic context, enabling users to pivot between related entities and trace actors or events.
Image Analysis and Multilingual Capabilities
This module includes an image analysis engine that processes images extracted from criminal sources, identifying logos, embedded text, screenshots of credentials, or compromised dashboard interfaces, thereby transforming images into actionable data. It also incorporates effective multilingual functionality.
Findings in Context
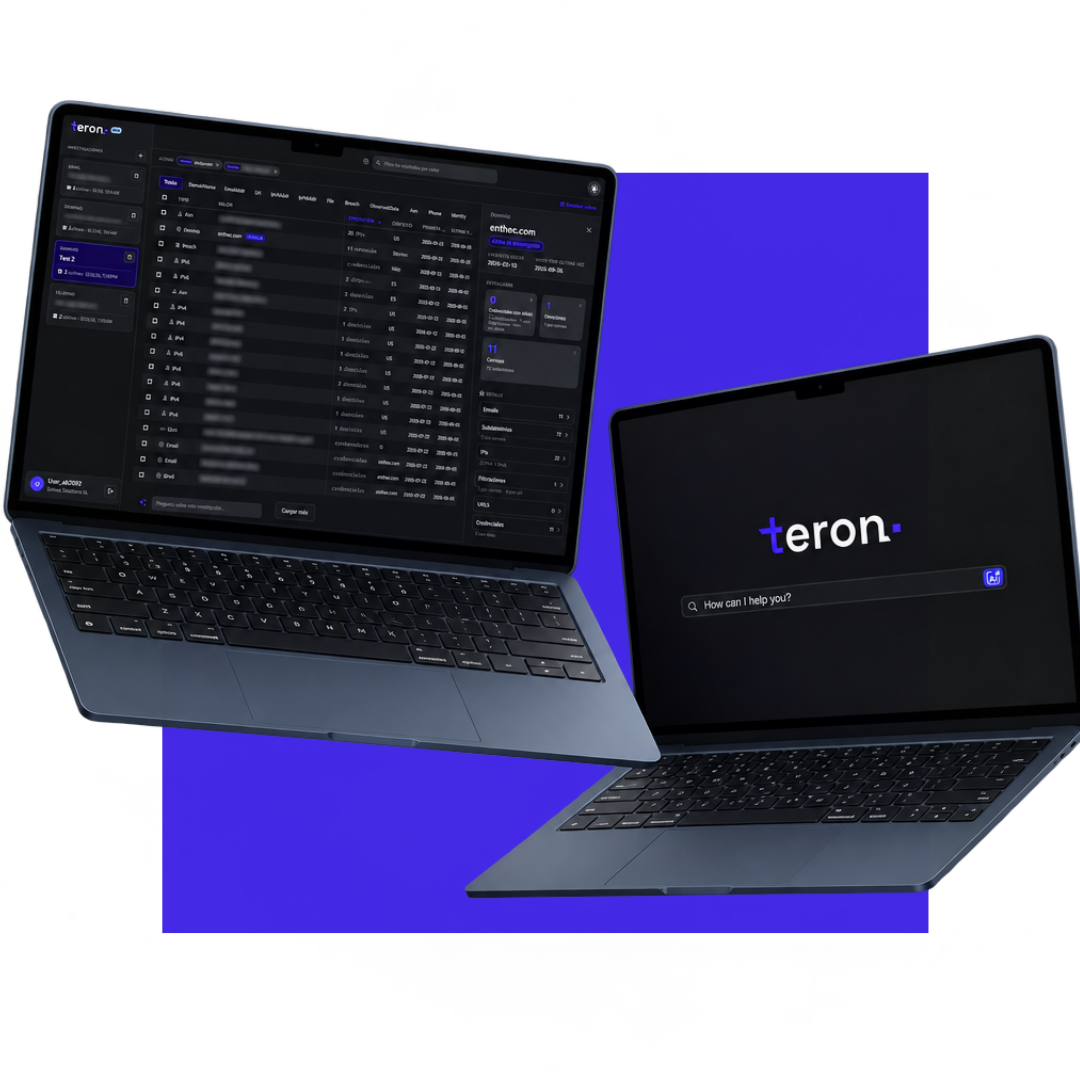
The analyst views the findings in a table (domain, credential, identity, email, subdomain), along with the first and last times they were detected, the number of occurrences, and the files in which they appear, and can filter them by type. From the details of each finding, the analyst can access the exposed data (leaked passwords, name, location, etc.) and see how it relates to other findings in the same investigation.
Ease of use
- Light mode and dark mode, with preferences saved across sessions and respecting the operating system's settings.
- Full support for Spanish and English, with the language taken from the user's profile.
- Accessible interface: keyboard navigation, labels for screen readers, and verified contrast ratios.
- Clear status indicators: the user always knows if something is loading, if it succeeded or failed, and why.
- Confirmation before deletion, with an explicit warning that the action cannot be undone.
Teron on the Enthec platform
Teron is not a standalone product: it’s part of a suite that shares sessions, design, and customers.
Continuous monitoring of an organization’s exposure profile.
Surveillance focused on people’s safety.
Thorough, in-depth investigation based on a specific piece of information.